Data protection

Kafka security for European enterprises

Mutual TLS and SASL secure connections, but EU enterprises still need stronger access controls, secret management, and audit trails.

Rated with a 4.5 from more than
13 G2 reviews

How we think about security

Security from the beginning.
It is part of the architecture.

You keep control.
Your data stays in your environment and jurisdiction.

Nothing is invisible.
Every governance action is logged and traceable.

European by design.
EU data protection standards are built in from the start.
The Kafka security gaps your auditor will find

DIY Kafka works until it doesn’t. Axual Streaming provides the operational stability, governance, and performance enterprise architects need not just at launch.

Credential management

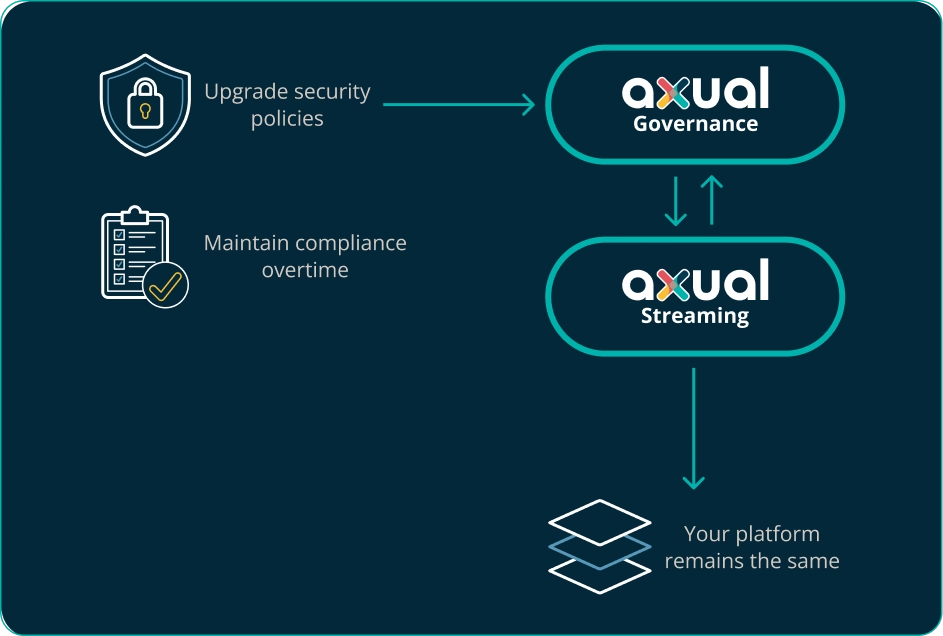
Update policies, workflows, and controls through configuration without disrupting data flows.

Multi tenant isolation

Kafka ACLs alone can fail to prevent teams from accessing data they should not see.

Compliance auditing

Authentication logs do not provide complete proof of who accessed what, when, and why.

End to end encryption

Securing brokers, clients, schema registries, REST proxies, and connector credentials requires consistent controls across every component.

Schema governance

Uncontrolled schema changes can break downstream systems. Production environments need compatibility rules and approval controls.

Governance across your streaming platform

Axual builds security into every layer, including identity and access, network isolation, and audit trails, from day one.

Enterprise IAM integration

Multi-cluster sync for topics, schemas, and offsets; HTTPS access via REST Proxy.

Fine grained RBAC

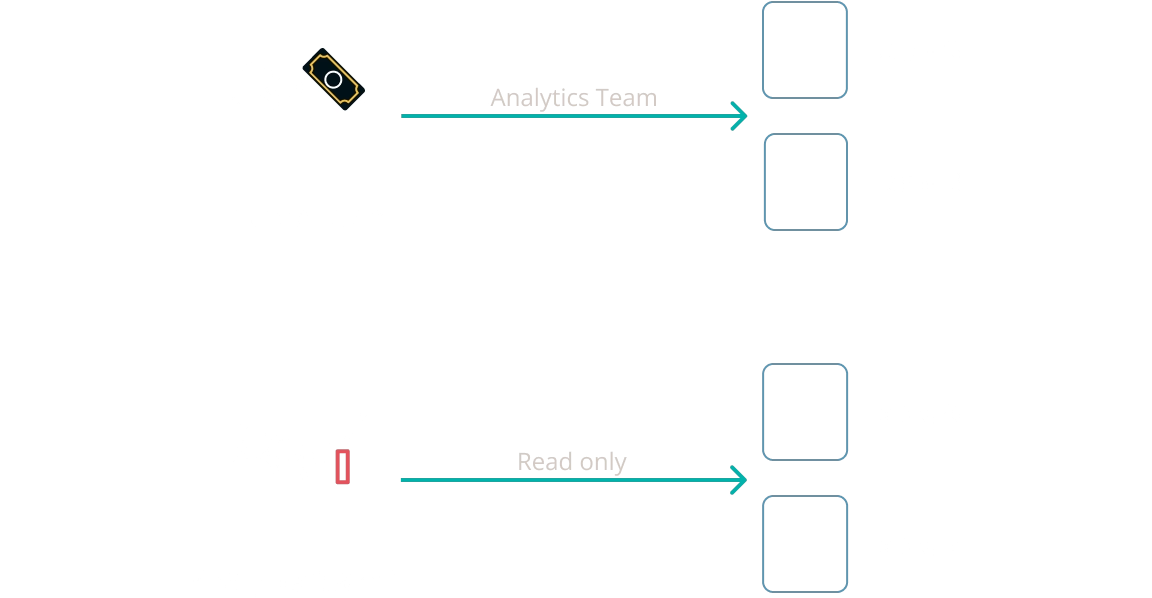
Axual controls access by team, environment, and operation. Finance can own payment topics, developers can have full access in development and read only access in production, and schema changes can require owner approval.

Vault based secret management

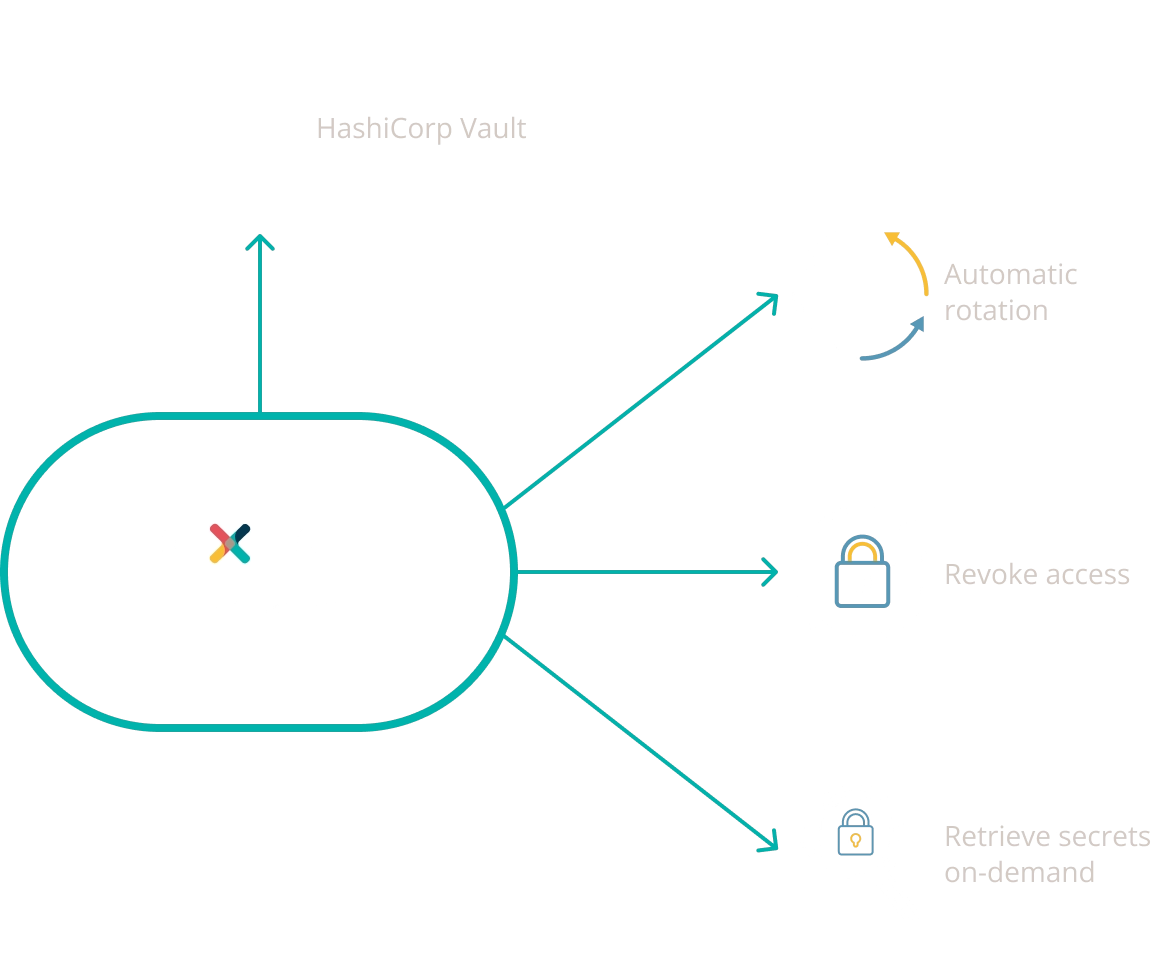
Credentials never appear in configuration files. HashiCorp Vault stores and rotates certificates, keys, and connector passwords. Infrastructure teams do not need access to production credentials.

Zero trust networking

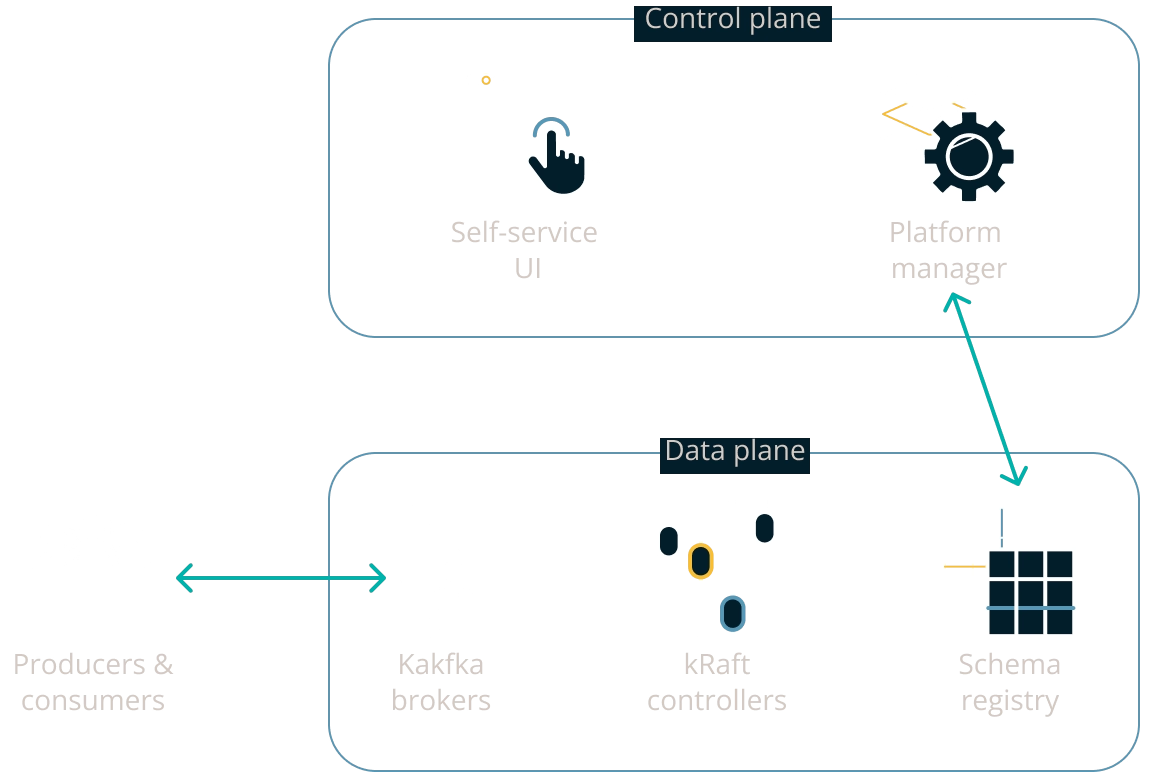
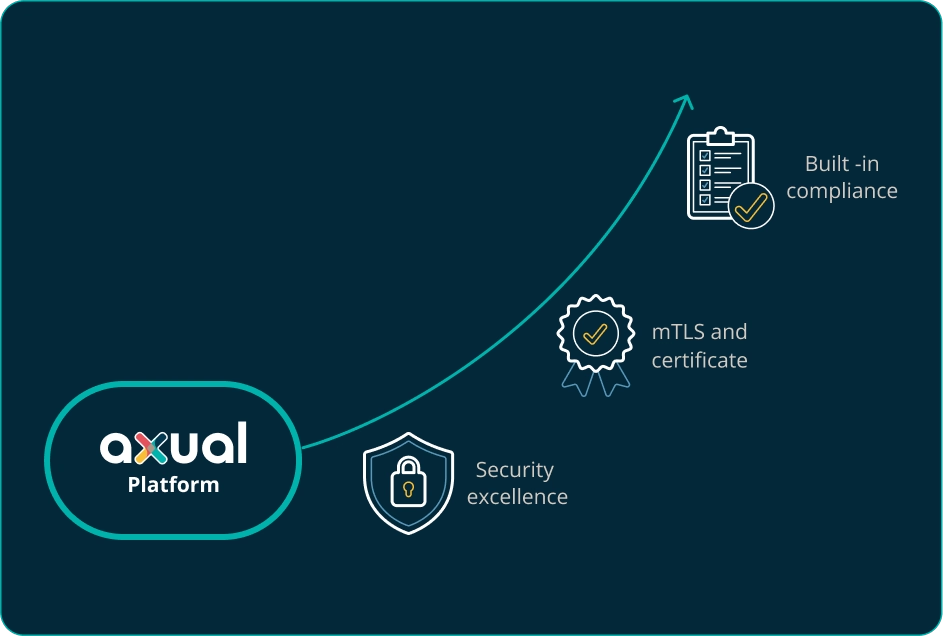
Network isolation, mTLS, certificate management, and separation between data and control planes protect each component. Each service is reachable only by the components that need it.

Built for European regulatory

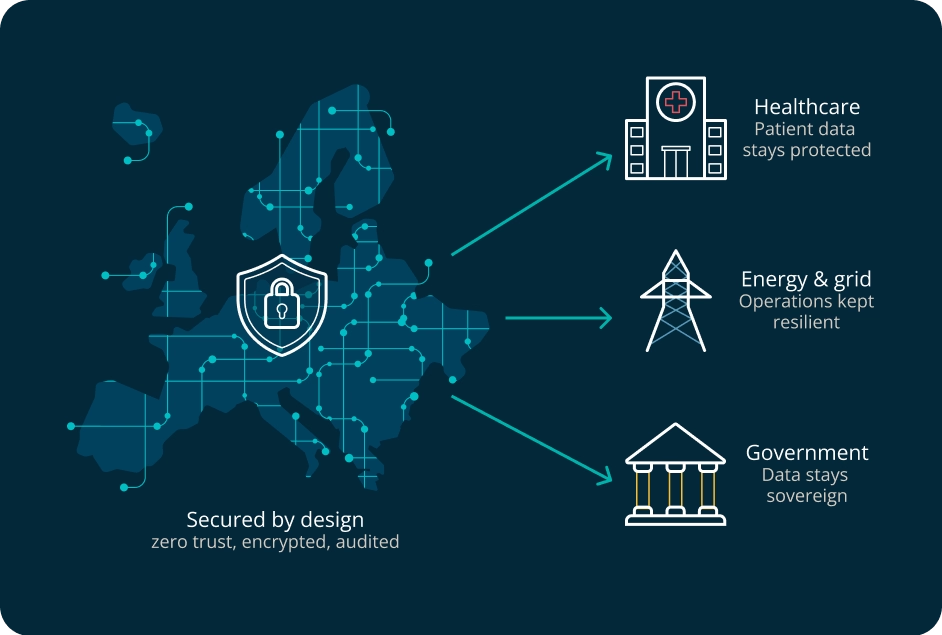
Financial services need MiFID II audit trails. Healthcare needs patient data controls. Energy needs critical infrastructure protection. Government needs data sovereignty guarantees.What this means in practice:

  • Data sovereignty by design
    Deploy on premises or in a private cloud to keep data in your jurisdiction.
  • GDPR aligned architecture
    Use role based access, audit logging, and encryption to support GDPR requirements.
  • Built and operated in Europe
    Axual is a European platform built for European regulatory needs.
  • Auditable by default
    Every access, approval, and provisioning action is logged automatically.
DORA
compliant
ISO 27001
compliant
GDPR
compliant
AICPA
SOC 2 Type II
View our ISO 27001 certification

Kafka security proven in production

Security requirements keep changing as EU regulations expand, threats evolve, and auditors demand more. Axual is designed to adapt without adding layers of patches.

Changing EU compliance demands

Update components independently and adjust security policies as financial, healthcare, and energy requirements evolve.

Governance without gridlock

Developers can create topics, generate credentials, evolve schemas, and deploy through CI/CD within defined controls. Every action is logged.

Where security matters most

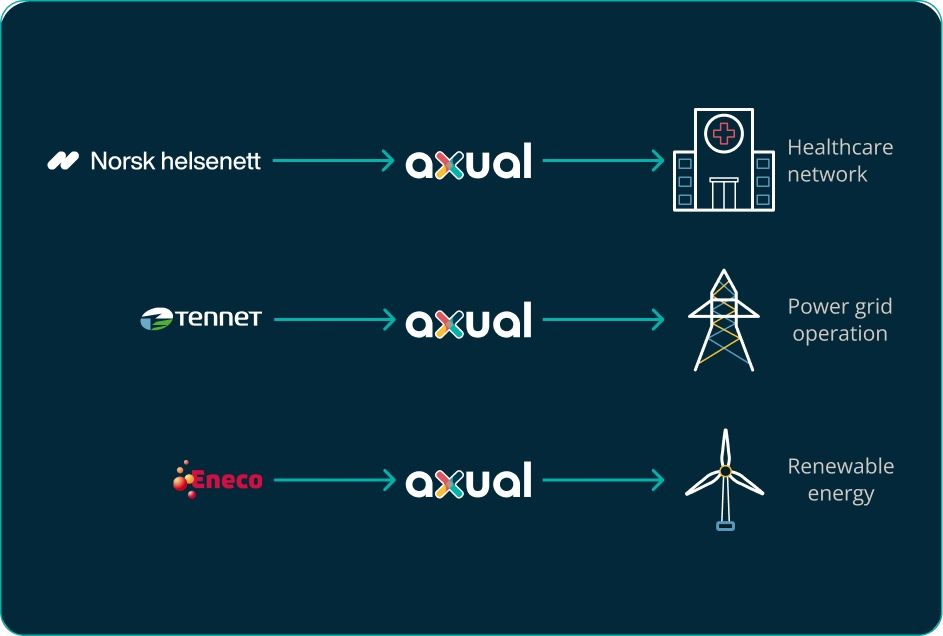
Norsk Helsenett, TenneT, and Eneco use Axual in production for healthcare, power grid, and renewable energy operations processing billions of events.

Security that supports growth

Automated credentials, certificate rotation, and built in compliance help teams move faster, reduce risk, and enter regulated markets.

"Data governance is critical at Rabobank. With Axual, we are able to see who has permission, who owns the data, or if the owner has given permission, and what the structure of the messages are."

Vincent Oostindle
Go to case study

"By having access to this real-time data, Eneco can use its data flexibly to help the organization and its customers even better."

Iem Smid
Go to case study

Event streaming for regulated industries

Discover why Europe's energy companies, financial services firms, and government agencies rely on Axual for mission-critical operations.

Energy

Grid stability, data exchange, and mission-critical reliability from a proven data streaming architecture that's trusted by leading TSOs, DSOs, and utility companies.

Read more

Healthcare

Control and compliance healthcare demands for critical clinical systems integration, patient monitoring, health information exchange, and population health analytics.

Read more

Government

Axual bridges the gap between real-time services and complete governance with secure data streaming for modern government infrastructure.

Read more

Frequently asked questions

How are secrets and credentials actually stored?

In HashiCorp Vault — never in configuration files, environment variables, or plaintext anywhere in the platform. Certificates, keys, and connector passwords are retrieved on-demand by the Axual Platform Manager, and rotate automatically without downtime.

How does Axual integrate with our existing identity provider?

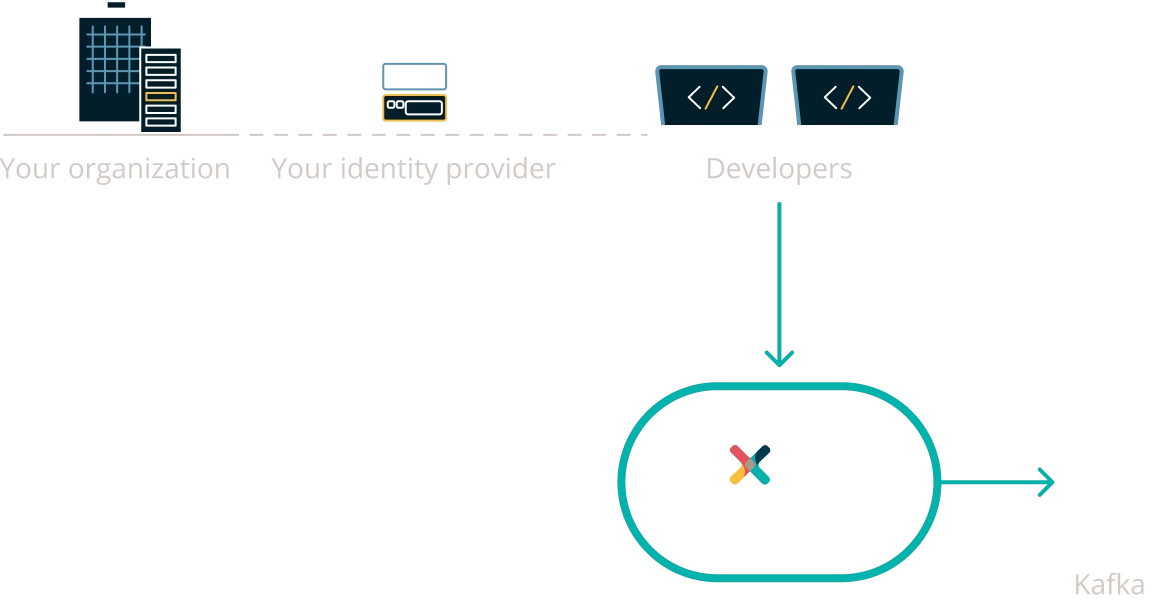
Through Keycloak. Your identity provider becomes Kafka's identity provider — users authenticate with corporate credentials, permissions sync from your existing AD/group structure, and your organization's password and MFA policies apply automatically.

What happens at the network level — is this zero trust, or perimeter security with extra steps?

Genuine zero trust: network isolation by design, mTLS everywhere with self-managing certificates, and a clean separation between the data plane and control plane. Components like ZooKeeper are reachable only where actually needed, not broadly exposed and access-controlled after the fact.

How does audit logging work — is this a real audit trail, or just authentication logs?

Every governance action is logged: topic and schema changes, access grants, connector deployments. This is designed to answer real audit questions (who accessed what, when, and under whose approval) — not just "who logged in."

Does self-service access provisioning weaken security?

No — it's scoped self-service. Developers can provision topics or request credentials instantly, but every action happens inside RBAC boundaries your organization defines, and every action is logged. Speed and control aren't a trade-off here.

Can we deploy entirely on-premises, or does any part of this require Axual's cloud?

Fully on-premises or private cloud deployment is supported end to end — identity, secrets management, RBAC, and audit logging all run within your own infrastructure.