Kafka governance

Discover, control and trust your streams

Axual Governance gives you visibility and control over ownership, schema changes, and access across every Kafka cluster.

Rated with a 4.5 from more than
13 G2 reviews

Keep bad data out of the stream

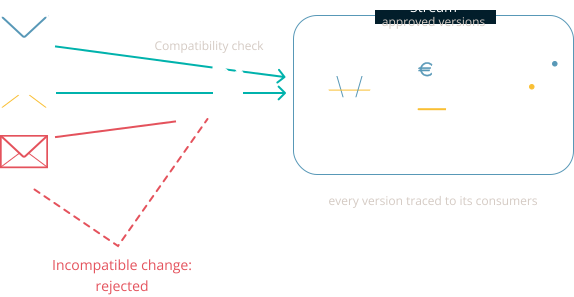
Schema registry governs your data before it causes a problem

  • Schema registry: A versioned repository that enforces backward, forward, or full compatibility across every topic
  • Compatibility validation: Incompatible schema changes fail during registration, before a consumer breaks in production
  • Version tracking with lineage: Every schema version is tracked, showing exactly which applications use each version
Axual access management with group-based permissions across environments

Find and own your streams without bottlenecks

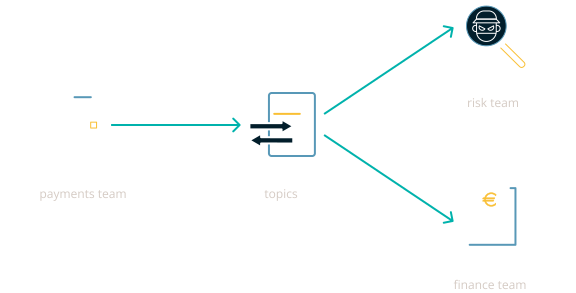
Self service topic and application management helps teams move faster.

  • Schema registry: A versioned repository that enforces backward, forward, or full compatibility across every topic
  • Compatibility validation: Incompatible schema changes fail during registration, before a consumer breaks in production
  • Version tracking with lineage: Every schema version is tracked, showing exactly which applications use each version
Axual schema management showing schema versions and compatibility rules

Prove control and adapt without rework

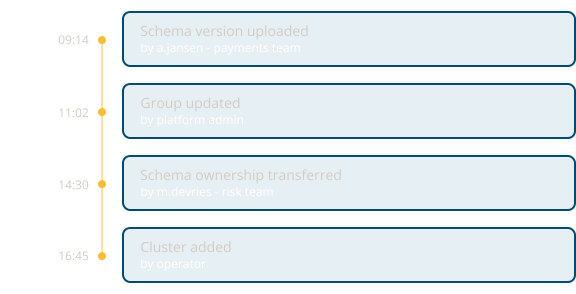
Audit trails and configurable policies help compliance evolve without architectural changes.

  • Immutable audit trail: Track every governance action for lineage and access history
  • Role based access control: Scale from small teams to thousands of users through group inheritance and delegated administration
  • Policy as configuration: Update policies, workflows, and controls without interrupting data flows or requiring migration
Axual audit history listing configuration and access-management events with filters

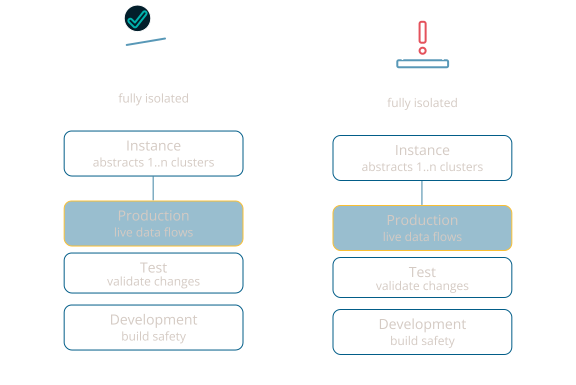
Isolate teams, environments, and instances without losing control

Tenant, environment, and instance separation give teams their own space without losing centralized control.

  • Tenant isolation: Give a team or business unit, like payments, its own fully isolated tenant, with the same granular access control and audibility as the rest of the platform
  • Environment separation: Split production from test and development resources, so teams can develop and validate changes without touching live data flows
Axual data masking applied to selected fields in topic browse

Core governance capabilities

A quick reference for everything above, capability by capability.

Capability
What it means
Role-based access control
Control who can create topics, deploy applications, and change configurations through groups and roles.
Schema registry
Manage schema evolution, enforce compatibility rules, and track every version with full lineage.
Audit trail
Track every governance action with immutable logs, for data lineage and access-history compliance.
API-first architecture
Automate governance through REST APIs or Terraform; integrate with CI/CD and GitOps workflows.
Connector management
Deploy Kafka Connect connectors with governance controls and full audit visibility.
Streaming applications
Run KSML applications with governance built into deployment and security.
Tenant & environment isolation
Give teams their own fully isolated tenant, and separate production from test/dev environments and instances, without losing centralized auditability.

Kafka governance in one place

Book a demo

Regulatory EU compliance by design

Meet regulatory requirements with audit trails, access controls, and data lineage.

Operational control at scale

Keep topics organized, enforce schema compatibility, and manage access as teams grow.

Governance that keeps up with regulation

Update policies, workflows, and controls through configuration without disrupting data flows.
Trusted in regulated environments

Discover why Rabobank, Eneco and ASN Bank depend on Axual to keep mission-critical operations compliant and running.

Rabobank

Read how Rabobank governs 600+ Kafka streams across 300+ teams while maintaining full GDPR compliance.

Read more

ASN Bank

ASN Bank replaced fragmented, siloed Kafka clusters with one centralized platform, onboarding 50+ development teams onto governed self-service without losing regulatory control.

Read more

Eneco

Eneco gives energy and customer teams self-service control over their own Kafka data flows, within governance boundaries that keep mission-critical operations secure.

Read more

Ready to bring control to your Kafka governance?

Frequently asked questions

How does the governance layer work independently from our Kafka clusters?

The control plane sits as a separate layer from your Kafka infrastructure — Confluent Cloud, Amazon MSK, or self-managed. Governance actions like creating topics or updating schemas never impact message flow, so producers and consumers keep processing while you address compliance gaps.

Can we use Axual alongside our existing Kafka or Confluent setup?

Your current topic naming conventions, ACLs, and operational procedures stay intact. Axual's governance layer wraps around existing deployments without migration or disruption, giving you centralized control across all clusters through a single pane of glass.

What happens to our existing Kafka governance when we implement Axual?

Axual Governance adds self-service, approval workflows, and audit history to existing Kafka clusters, so you can improve governance first and decide about migration later.

How does role-based access control scale from pilot to production?

RBAC maps to your organizational structure through groups and roles. Start with basic roles for a pilot team of ten; as you scale to hundreds of users, the same model extends through group inheritance and delegated administration.

Can we maintain our GitOps workflows with Axual governance?

Yes. The Axual Terraform provider treats governance as code — topics, schemas, applications, and access controls become declarative resources your existing CI/CD pipelines deploy, review, and roll back like any other infrastructure.

How does Axual ensure compliance with evolving regulations?

Every governance action creates an immutable audit trail. Schema versioning tracks data-structure evolution for lineage requirements, and role-based access satisfies segregation of duties. When regulations change, you update policy through configuration, not architecture.

What's the operational overhead of running a separate governance layer?

Less than managing governance manually across multiple Kafka clusters. The control plane runs on Kubernetes with horizontal scaling and automated failover — your Kafka clusters keep operating normally during governance maintenance.

How does schema management prevent breaking changes in production?

Axual enforces schema compatibility rules before changes reach Kafka. Incompatible changes fail at registration, not when a consumer breaks in production, and every schema version is tracked with full lineage.

Does Axual governance work with our existing identity provider and security policies?

Yes — via OIDC or SAML, whether that's Active Directory, Azure AD, or another enterprise IdP. Users authenticate with existing credentials and inherit group memberships; service accounts use JWT tokens for automation, and sensitive credentials stay in HashiCorp Vault.